標題搜尋:
⭠ 左右滾動 ⭢
- Invicti - Web + API 網頁弱點掃描平台
-
類別資訊資安軟體
-
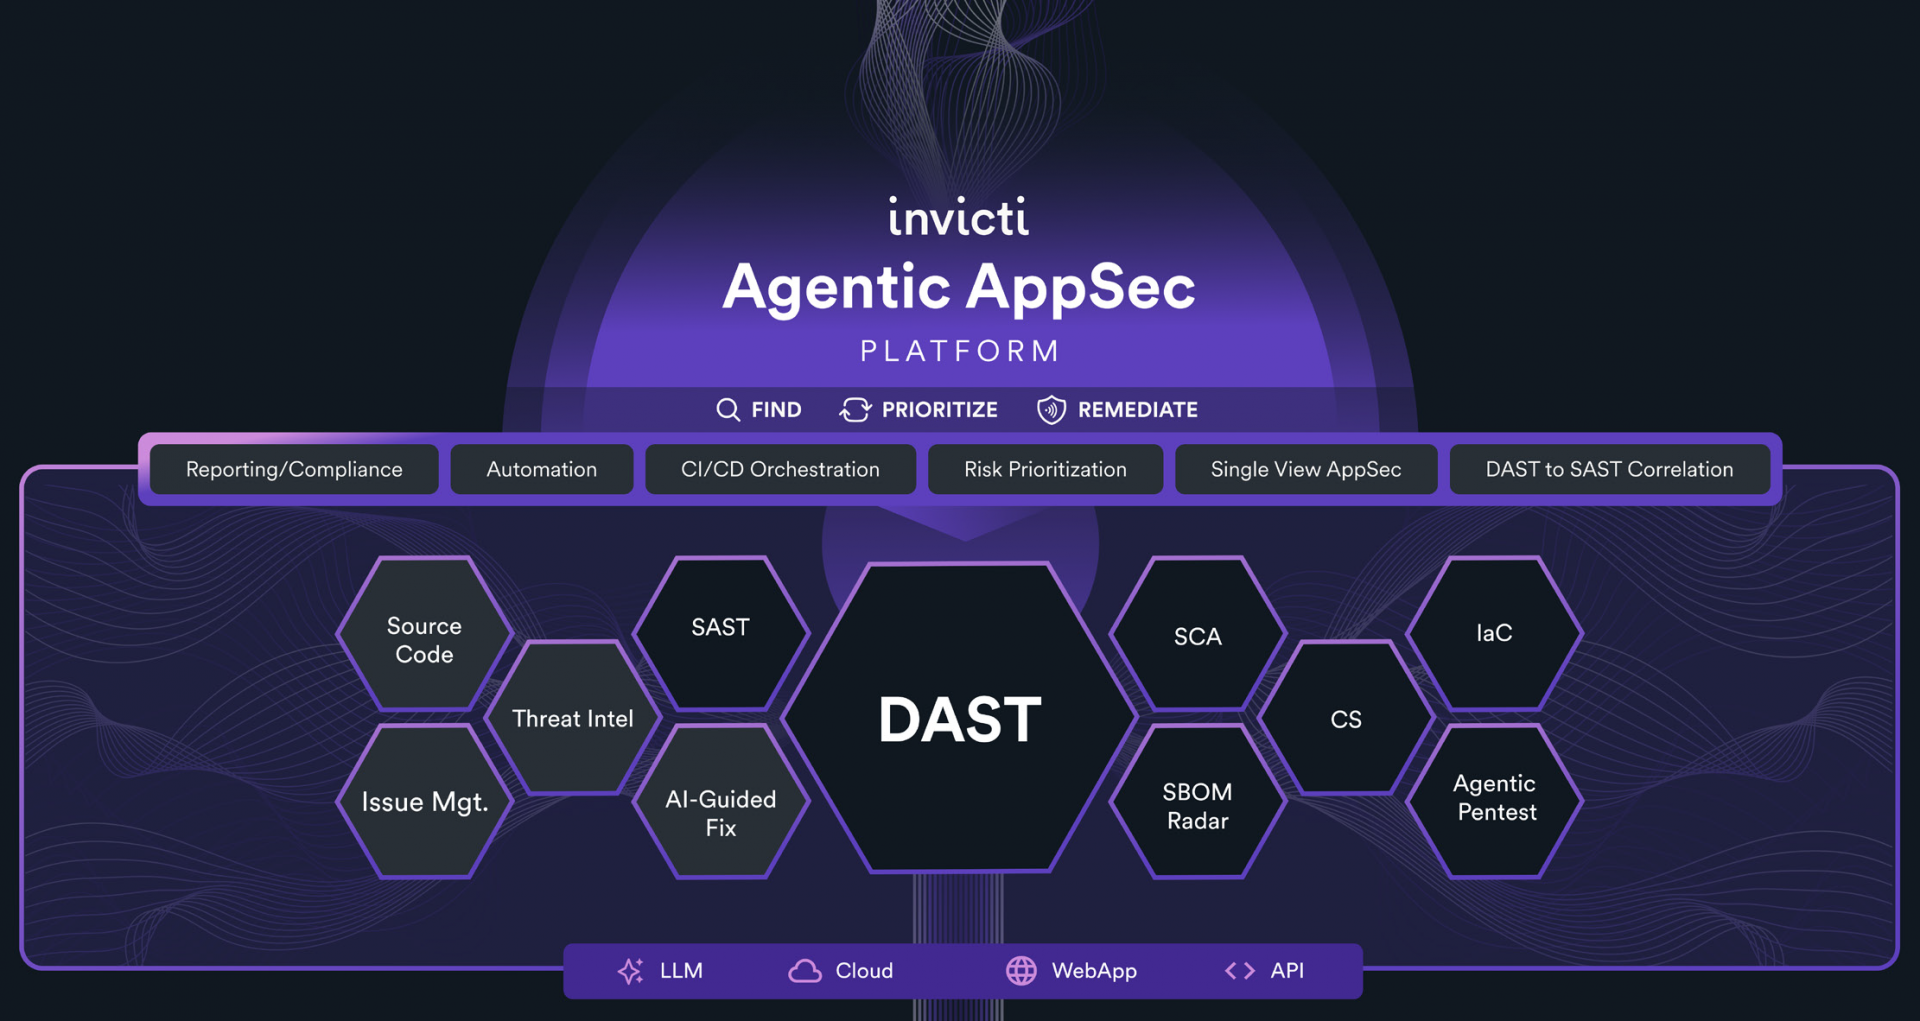
介紹Invicti(整合原 Acunetix 與 Netsparker 技術)是全球領先的應用程式安全平台,致力於協助企業實現 AppSec(應用程式安全)自動化與規模化。Invicti Web + API 是一個結合動態應用程式安全測試(DAST)與 API 安全防護的整合型平台。透過獨家的 Proof-Based Scanning™ 概念驗證技術與 AI 輔助分析,它能從單一管理介面自動盤點所有網頁與 API 攻擊面、精準驗證真實漏洞並過濾誤報,且排列運行時(Runtime)風險的優先順序。該平台提供全面涵蓋 Web 與 API 的可視性與控制權,協助資安與開發團隊徹底消除資安雜訊,實現持續、無縫的應用程式安全防護。
Invicti - Web + API
- Industry-Leading DAST + IAST with Proof-Based Scanning™
Powered by Invicti’s core Dynamic Application Security Testing technology, you no longer need to waste time manually verifying false positives. Once a vulnerability is detected, Invicti automatically simulates a real-world attack to confirm its exploitability.
• Proof-of-Exploit Verification: Automatically triggers safe, read-only proof-of-concept exploits on suspected vulnerabilities to confirm real-world exploitability, delivering up to 99.98% accuracy.
• Zero False Positives & No Manual Triage: Eliminates manual false-positive verification, allowing security and development teams to immediately focus on remediating genuine, high-risk threats.
• Modern Web & AI-Guided Scanning: Fully supports HTML5, Single Page Applications (SPAs such as React, Angular, and Vue), and complex authentication mechanisms (OAuth2, JWT, SSO). Leverages AI to seamlessly navigate business logic and bypass CAPTCHAs.
• Interactive Application Security Testing (IAST): Uses embedded IAST agents deep within the application runtime to pinpoint vulnerabilities down to the exact line of code and SQL query, accelerating diagnosis.
- Comprehensive API Security
As microservices and cloud architectures expand, APIs have become a primary attack surface. Invicti Web + API delivers deep, proactive API defense.
• Broad Protocol & Specification Support: Covers RESTful, GraphQL, and SOAP/WSDL architectures, with direct ingestion of OpenAPI (Swagger) specifications and Postman Collections.
• Multi-Layer Automated API Discovery: Automatically uncovers unmanaged Shadow APIs and abandoned Zombie APIs, completely eliminating security blind spots.
• Dedicated OWASP API Top 10 Coverage: Deeply tests for critical logic vulnerabilities, including BOLA/IDOR (Broken Object Level Authorization), BFLA, unauthorized access, and excessive data exposure.
- Continuous Asset Discovery
You cannot secure what you do not know exists. Invicti’s continuous discovery engine proactively identifies and tracks all web and API assets across your organization.
Automate regular scans – so you can be confident you’ll catch new vulnerabilities quickly.
• Uncover Forgotten Assets: Automatically discovers forgotten subdomains, staging/test environments, public-facing services, and idle applications.
• Visual Asset Management: Delivers a unified dashboard that provides real-time visibility into the security posture of all external web and API assets, allowing you to onboard them into scheduled scans with a single click.
- AI-Assisted Automated Vulnerability Prioritization
Provides code-level remediation guidance and leverages AI to filter out alert noise, helping developers remediate flaws faster.
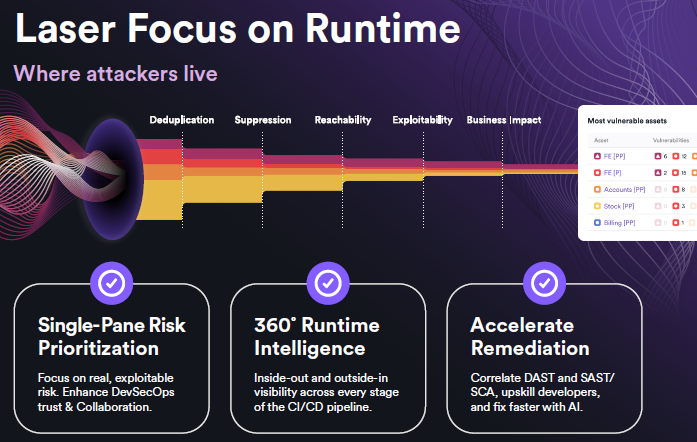
• AI-Driven Risk Analysis: Analyzes vulnerability reachability, exploitability, and business impact to present an actionable list focused strictly on real, impactful risks.
- Predictive Risk Scoring
Leverages extensive historical data and AI analytics to grade and prioritize risk profiles across all web applications and APIs.
• Actionable Prioritization: Helps security teams identify high-risk applications and severe vulnerabilities first, ensuring resources are concentrated on the most pressing threats.
- Seamless DevSecOps Integration
Shifts security testing left, identifying vulnerabilities early during the development and testing phases.
• Bi-Directional CI/CD & Ticketing Integration: Offers native integrations with leading enterprise platforms, including Jira, GitHub, Jenkins, Azure DevOps, GitLab, and ServiceNow.
• Automated Workflows: Automatically logs tickets for verified vulnerabilities directly to developers. Once fixed, re-testing is automatically triggered with zero human intervention required.
- Compliance Reporting
Includes built-in report templates for major international security standards, generated with one click for effortless audits and vendor security assessments.
• Supported Frameworks: PCI DSS, OWASP Top 10, OWASP API Top 10, HIPAA, ISO 27001, GDPR, CWE/SANS, and more.
Why Choose Invicti Web + API?
• Unmatched Accuracy: Drastically reduces false positives using patented Proof-Based Scanning™, saving teams hundreds of hours in manual verification.
• High Scalability: Effortlessly scales and provides centralized management, whether securing a single web application or managing thousands across a global enterprise.
• Unified Single Platform: Breaks down silos between web and API scanning, delivering total visibility and control over modern applications and runtime security risks from a single pane of glass.
About Invicti & Official Taiwan Distributor – NFI Co., Ltd.
Invicti is a global application security leader formed by combining two world-renowned security powerhouses: Netsparker (celebrated for its industry-leading technology) and Acunetix (recognized for its broad market adoption). Focused on addressing the growing risks associated with Web and API attack surfaces, Invicti is an industry pioneer in automated web security and Dynamic Application Security Testing (DAST).
Invicti is trusted globally by cybersecurity experts, SMBs, and large enterprises. It remains the preferred choice for government entities, defense sectors, educational institutions, telecommunications providers, banks, financial institutions, and e-commerce leaders—including the U.S. Department of Defense and Fortune 500 companies such as Nike, Disney, and Adobe.
In Taiwan, NFI Co., Ltd. (新永資訊有限公司) serves as the official authorized distributor, providing localized product consulting, technical support, and licensing services.
系統需求
Minimum System Requirement
- - Supported Operating systems
- Microsoft Windows 2016 R2 and later、Windows 11、10
- Ubuntu Desktop/Server 18.0.4 LTS or higher
- Suse Linux Enterprise Server 15
- Kali Linux versions 2019.1 and later
- CentOS 8 and CentOS Stream Server and Workstation (with SELinux disabled)
- RedHat 8 and 9 (with SELinux disabled)
- Oracle Linux 8 (with SELinux disabled)
- *We are actively testing other Linux distributions.
- Please let us know if you have requests for specific distros.
- - CPU: 64 bit 2 core CPU processor
- - System memory: minimum of 4 GB RAM
- - Storage: 50 GB of available hard-disk space.
*This does not include the storage required to save the scan results, which will depend on the level of usage of Acunetix. - - Supported Browsers: Firefox、Chrome、Edge、Safari.
Invicti - Web + API
- 業界領先的DAST + IAST 與 Proof-Based Scanning™ 驗證技術
Invicti 核心的動態應用程式安全測試技術,不再浪費時間人工過濾誤報!Invicti 發現漏洞後會自動模擬駭客攻擊進行驗證。
• 自動概念驗證(Proof-of-Exploit): 對可疑弱點自動發起安全的「唯讀式概念驗證」,確認漏洞是否真能被利用,提供高達 99.98% 的精準度。
• 零誤報與免人工分流: 徹底省去手動驗證誤報的時間,讓開發與資安團隊能立即投入真正高危威脅的修復。
• 現代 Web 與 AI 導航掃描: 完整支援 HTML5、單頁應用程式(SPA,如 React、Angular、Vue)、複雜身分驗證機制(OAuth2、JWT、SSO),並透過 AI 輕鬆解析商業邏輯與驗證碼(CAPTCHA)。
• 交互式應用安全測試 (IAST):結合 IAST Agent 深入應用程式運行時內核,精準定位弱點在源代碼中的具體行數與 SQL 查詢,加速診斷。
- 全面 API 安全檢測 (API Security)
隨著微服務與雲端架構普及,API 成為駭客的主要攻擊目標。Invicti Web + API 提供深入且主動的 API 安全防護。
• 支援主流協議與規範:涵蓋 RESTful, GraphQL, SOAP/WSDL 等架構,並支援直載 OpenAPI (Swagger) 與 Postman Collections。
• 多層次 API 自動探索:自動挖掘未被列管的「影子 API (Shadow APIs)」與廢棄的「殭屍 API (Zombie APIs)」,消除安全盲區。
• OWASP API Top 10 專屬防護:深度檢測 BOLA/IDOR(物件層級授權失效)、BFLA、未授權存取及敏感資料過度暴露等邏輯漏洞。
- 持續資產發現 (Asset Discovery)
您無法保護您不知道的資產。Invicti 的持續探索服務能主動盤點與維護屬於貴公司的 Web 與 API 資產。
• 找出遺忘資產:自動偵測被遺忘的子網域、測試站點、對外服務及閒置的應用程式。
• 可視化資產管理:提供統一儀表板,即時掌握所有對外 Web 與 API 資產的安全態勢,並能一鍵納入排程掃描。
- AI 輔助的漏洞自動化優先級排序
直接提供程式碼層級的修復指引,利用 AI 技術自動過濾警報雜訊,幫助開發人員加速漏洞處理。
• AI 漏洞風險分析:利用 AI 分析漏洞的可達性 (Reachability)、可利用性 (Exploitability) 及業務影響,僅列出真正具有脅迫力的「真實風險清單」。
- 預測性風險評分 (Predictive Risk Scoring)
利用海量歷史數據與 AI 分析,為您的 Web 應用程式與 API 進行風險評級與優先順序分類。
• 優先順序處置:協助資安團隊判斷哪些漏洞或應用程式具有最高風險,優先集中資源處理最緊迫的威脅。
- 無縫整合 DevSecOps 流程
將資安測試「左移 (Shift Left)」,在開發與測試階段即發現漏洞。
• 雙向整合 CI/CD 與工單:原生支援 Jira, GitHub, Jenkins, Azure DevOps, GitLab, ServiceNow 等主流工具。
• 自動化工作流:發現驗證漏洞自動開單給開發人員;修復後可自動觸發複掃 (Retest),完全無需人工介入。
- 合規性報告 (Compliance Reports)
內建多種國際資安標準報告模板,一鍵生成,輕鬆應對稽核與客戶要求。
• 支援標準:PCI DSS, OWASP Top 10, OWASP API Top 10, HIPAA, ISO 27001, GDPR, CWE/SANS 等。
為什麼選擇使用 Invicti Web + API?
• 極致精準度: 透過獨家專利 Proof-Based Scanning™ 證據式掃描大幅降低誤報,節省團隊數百小時的人工驗證時間。
• 高擴充性: 無論是單一網站還是擁有數千個應用程式與 API 的大型企業環境,皆能輕鬆彈性部署與集中管理。
• 單一平台涵蓋: 打破 Web 掃描與 API 掃描的資訊孤島,於單一平台完全掌控現代應用程式與運行時的資安風險。
關於Invicti原廠與台灣代理商-新永資訊
Invicti 是一間結合「技術最強 (Netsparker)」與「市佔最廣 (Acunetix)」兩大國際知名廠牌而成的應用程式資安巨頭。主要專注於日益俱增的 Web 與 API 攻擊風險,Invicti 也是自動化 Web 安全技術與動態測試(DAST)的先驅與業界領導者。Invicti 產品深受全球個人資安專家、中小型企業與大型機構組織的信賴,更是政府、軍事、教育、電信、銀行、金融和電子商務等機構的首選,客戶包含五角大廈與全球 500 大企業(如 Nike、Disney、Adobe 等)。
Invicti 在台灣的專業代理商為「新永資訊有限公司(NFI Co., Ltd.)」,提供在地化的產品諮詢、技術支援與授權服務。
Invicti - Acunetix 網頁弱點掃描
Acunetix 是由 Invicti 開發的一款強大又聰明的網站安全掃描工具,能自動幫你找出網站、Web 應用程式和 API 裡的安全漏洞。它內建業界頂尖的爬蟲與掃描引擎,不只能自動建立網站資產清單,還能偵測像 SQL 注入、跨站腳本 (XSS) 這類常見高風險的問題。 Acunetix 使用 Invicti 的先進技術與漏洞資料庫,能「實際驗證」漏洞是否真實存在,大幅減少誤報,讓資安團隊能專注處理真正的風險。它同時支援與各種開發管理工具(如 Jira、GitLab、Azure等)整合,方便追蹤與修補漏洞。對網站管理員、資安工程師或 DevSecOps 團隊來說,Acunetix 不只是掃描工具,更是全天候守護網站安全的可靠夥伴。
CANVAS 網頁安全測試工具
Immunity 的 CANVAS 為全球的滲透測試人員和安全專業人員提供了數百個漏洞利用、一個自動化漏洞利用系統和一個全面、可靠的漏洞利用開發框架。
趨勢科技 PC-cillin 2026 雲端版
PC-cillin 雲端版採用 XGen 多層式防禦技術,融合先進的 AI 人工智慧,為您預先防範各種以竊取個資金錢為目標的各種安全威脅,包含勒索病毒和網路詐騙等,全面守護您的上網裝置與個資安全。